Survey Reveals Budget Shifts Amid Rising AI Risks
\nA global survey conducted by PwC indicates that corporate leaders are significantly increasing their focus on artificial intelligence-related security challenges. The firm’s 2027 Global Digital Trust Insights Survey found that 84 percent of corporate respondents expect cybersecurity budgets to expand to meet potential AI threats.
\nThis figure represents an increase from 78 percent in 2025, according to the reported data. The survey captured views from almost 4,000 business and technology executives across 71 countries and territories.
\nAmong security leaders specifically, 58 percent ranked AI as a top priority for their cybersecurity budgets in the upcoming year. This prioritization coincides with the rollout of frontier AI models. Half of the security leaders surveyed identified attacks targeting AI systems among their top threats.
\nThese AI-focused threats were ranked higher than other common concerns, including cloud-related threats at 40 percent, third-party breaches at 34 percent, and ransomware at 33 percent.
\n\nLeadership Gaps in Governance and Preparedness
\nDespite the projected budget increases, the survey highlighted significant gaps in organizational preparedness and governance. PwC’s data showed that 50 percent of respondents identified attacks targeting AI systems as among the cyber threats they are least prepared to address.
\nTrust in automated defense mechanisms remains low. Only 22 percent of survey respondents said they would authorize fully autonomous AI agents for cyber defense.
\nThe research also pointed to a disconnect between risk awareness and board-level engagement. Less than half of the respondents, specifically 47 percent, strongly agreed that cyber risk is a standing agenda item at the Board level.
\nOperational continuity plans also lag behind threat expectations. Only 39 percent of security, risk, and operations leaders reported having a fully formalized and integrated operational continuity plan that specifically addresses cyber risks.
\n\nData Risk Implementation Shortfalls
\nImplementation of specific data protection measures was found to be incomplete across the surveyed organizations. Companies have implemented, on average, only three out of seven key data risk measures.
\nOnly 5 percent of respondents reported having fully implemented every data risk measure. Additionally, 33 percent of chief executives and security and risk leaders stated that their companies have established dedicated AI roles, such as a chief AI officer or an AI board.
\n\nStrategic Recommendations for Risk Management
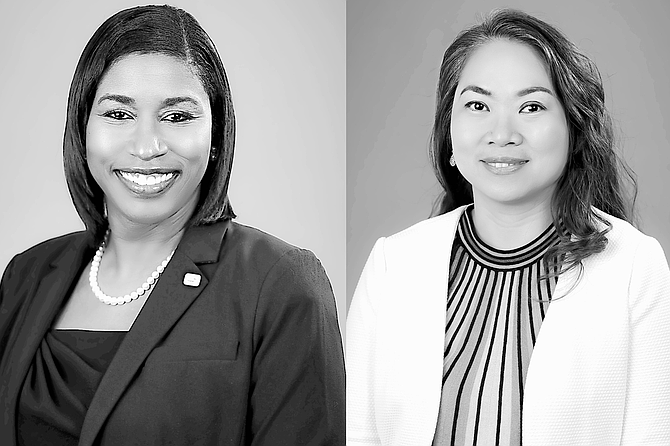
\nMyra Lundy-Mortimer, territory assurance leader and risk assurance partner for PwC Bahamas, warned that the emergence of AI-driven threats is creating a new level of complexity for organizations. She noted that this occurs at a time when many companies are still strengthening their broader cyber resilience capabilities.
\nLundy-Mortimer stated that leaders must move beyond viewing cybersecurity solely through a technology lens. She emphasized that cyber risk must be considered as part of enterprise-wide decision-making.
\nNestle Maullon, PwC Bahamas risk assurance director, added